
What Fable 5 Is: A High-Capability Model With Firm Guardrails
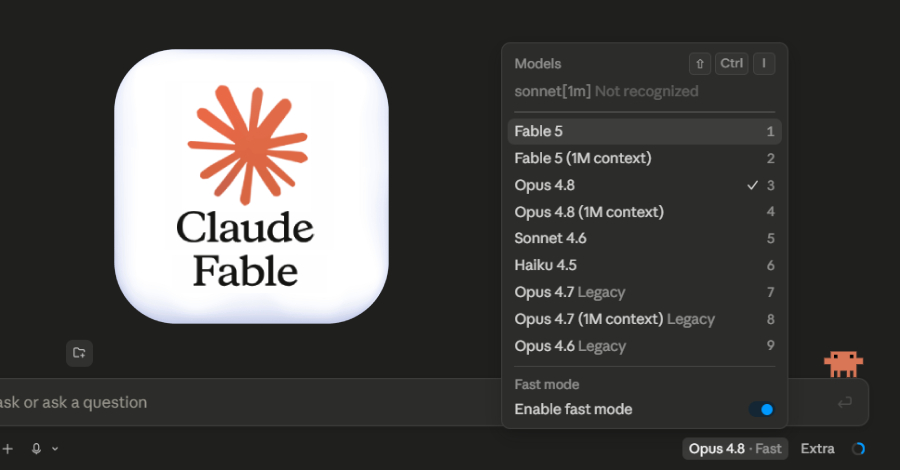
Fable 5 is Anthropic’s Mythos-class public model that combines long-horizon autonomous reasoning, improved coding skills, and stricter enterprise AI guardrails into a single system designed for both advanced development and safer operations. It is paired with Mythos 5, a gated version with some safeguards relaxed for security and research users. Benchmarks suggest Fable 5 is state-of-the-art and, in community testing, often outperforms Opus 4.8 on complex programming and debugging tasks. One Hacker News user reports that “Fable on ‘high’ is producing substantially better results than Opus 4.8 on xhigh.” The model is available via the Claude API, major cloud platforms, and Anthropic’s own surfaces. However, Anthropic links this power to tighter controls over safety, data retention, and access, which reshapes how enterprises must think about AI data retention policy, vendor risk management, and acceptable operational constraints.
Security Guardrails and Fallback Behavior: Safety as a Service
Fable 5 security features are built around a provider-controlled safeguard layer. For sensitive topics in cybersecurity, biology, and chemistry, Fable 5 may block a request and automatically route it to Opus 4.8, with users told that a fallback occurred. Anthropic says this safety switch activates in under 5% of sessions and is tuned conservatively, so some harmless requests will be caught. Mythos 5 shares the same core model but removes some of these controls for vetted Glasswing partners and select security and research teams. This means enterprises depend on safeguards they do not operate: Anthropic defines the scope, sensitivity, and reliability of the model-level controls, while organizations must still add their own runtime security and enterprise AI guardrails in applications. The result is a shared-responsibility model where safety monitoring lives both at the vendor layer and within enterprise security stacks.
Thirty-Day AI Data Retention Policy: New Risk and Compliance Questions
The biggest structural shift is Anthropic’s mandatory 30-day AI data retention policy for all Fable 5 and Mythos 5 traffic, covering both prompts and completions. This requirement overrides prior zero-retention data processing agreements for any Mythos-class usage and offers no opt-out. According to Forrester, Anthropic states that retained data is not used to train new Claude models, not used for nonsafety purposes, is subject to logged human access, and is deleted after 30 days in almost all cases. The official rationale is defensive: detecting novel attacks, multirequest abuse, jailbreaks, and reducing false positives in the safeguard layer. However, the 30-day window also aligns with an executive order framework around voluntary frontier model sharing, which brings potential government visibility into scope. CISOs must now reassess data classification, model selection, and which workloads can tolerate this retention requirement.
User Frustration: Burn Rate, Usage Limits, and Operational Constraints
Even as Fable 5 wins praise for coding and reasoning performance, early adopters are running into usage and cost friction. Anthropic lists prices at USD 10 (approx. RM47) per million input tokens and USD 50 (approx. RM236) per million output tokens, with free access for some subscriptions only until June 22 before usage credits are required. Community users report that the model burns through quotas quickly compared with Opus 4.8. One Max20 subscriber wrote that usage climbed to almost 2% per minute doing similar work, while another reported going from 0 to 43% of their limit within minutes. These burn-rate issues mean that even though Fable 5 may “feel” smarter and more efficient, its practical value depends on how teams manage token budgets, throughput needs, and the trade-off between premium capability and sustainable operating costs.
Implications for Enterprise Adoption and Vendor Risk Management
For CISOs and procurement leaders, Fable 5 changes the adoption calculus. On one side, it offers top-tier coding benchmarks, stronger safeguards, and an integrated AI data retention policy tuned for safety monitoring. On the other, enterprises must accept mandatory 30-day retention, vendor-managed guardrails, model fallback behavior, and higher burn rates that strain budgets and usage limits. This combination shifts vendor risk management from a pure SLA and price discussion to a deeper analysis of governance, auditability, and lock-in. If key workloads depend on Fable 5’s specific safety layer and performance profile, switching providers becomes harder. Organizations will need clear model selection policies, internal guardrails that complement Anthropic’s controls, and cost-optimization strategies that decide when Fable 5’s power is warranted and when a cheaper or more flexible model is enough.